We not keep
your briefs
Briefs can contain unreleased campaigns, client strategy, budgets and decisions that have not been announced yet. NoBS protects that work with application-layer encryption, account-scoped storage and a deliberately small data footprint.
Encrypted
AES-256-GCM
Brief content is encrypted
before storage.
Content-free
logging
Operations are logged.
Brief ideas are not.
No saved
archive
Original uploads are
not kept as files.
Server-side
identity
Your account is part of
the record address.
Protection
at every
boundary
NoBS uses different controls for transmission, processing, storage and access. The goal is not to hide the architecture. It is to make each boundary explicit.
You submit
your brief
Typed, pasted or uploaded through
a protected HTTPS connection.
NoBS processes
the brief
The content is handled automatically
for the task you requested.
Required
services
Only the providers needed to generate
the result receive relevant data.
Content is
encrypted
A per-record AES-256-GCM
envelope is applied before storage.
Account-scoped
storage
The verified user and project
identity resolve the stored record.
The datastore
receives the
encrypted side
NoBS does not rely on the storage provider for this. Brief content and derived output are encrypted by the application before they are written to the datastore.
Readable during authorized processing

Encrypted
before
storage
8fd2c9a16a80b9c7db0f1a5d52d7049f7a908f64bf718218306aa17fc9bc401e5d87dc4b41f970ce8a77d561b0b785aa6a34d3cb2114e11f3e9eb627f51e90a2f98d01d0ab37cf02d8a1f78d2a10359b51f839a177865e14840ba9c11df73c9900d8234a5c8a7ef66a63071bb499cef96f16524edcbe59c43fcab913ff038a93
Authenticated encryption protects confidentiality and helps detect modification of the encrypted record.
original-file
archives
Uploaded documents are parsed during the request. Extracted text is encrypted into the brief record, and NoBS does not create a permanent public file URL for the original upload.
YOUR RESULTS
NoBS generates your Result and Report to complete your request. We don't create separate copies of them, build a content archive from them, or place your generated content in our logs.
CONTENT FOR
AI TRAINING
NoBS does not use your briefs or generated outputs as training data. AI processing is provided through the OpenAI API, where API data is not used to train models by default. NoBS keeps optional data-sharing disabled and does not opt in to model training or improvement.
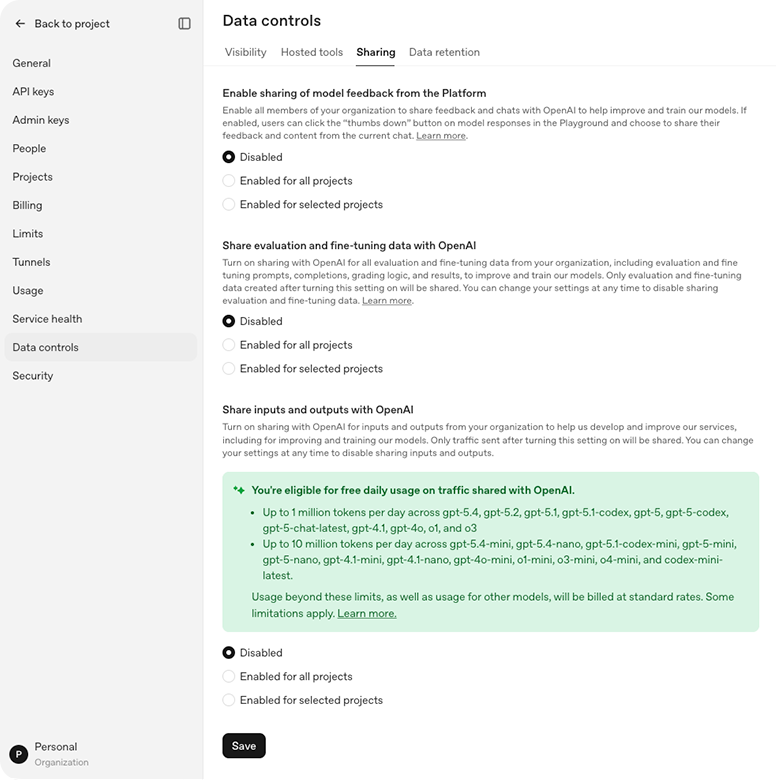
OpenAI API data-sharing controls for NoBS.
All optional sharing is disabled.
Your account
is part of
the address
NoBS does not retrieve a global project first and then apply a visual ownership filter. The verified account identity participates in resolving the record.
The illustration is conceptual and intentionally does not expose production key structures.
Process it
Extract it
Remove the
original file
NoBS is built around brief content,
not around maintaining
a permanent document library.
Upload
Supported document reaches the request.
Parse
NoBS reads the file format.
Extract
Relevant text is extracted.
Encrypt
Content enters the protected brief record.
Remove
The original upload is not retained as a permanent NoBS file.
The system knows
the job ran
It does not need
to log what
the job said
NoBS logs operational metadata to understand whether a process succeeded, failed or took too long. Brief content and generated output are excluded from application logs.
Logs can
contain
Logs do
not contain
Security
without the
theater
Specific controls are more useful than vague promises.
These are the protections NoBS can describe directly.
| Control | NoBS implementation | Status |
|---|---|---|
| Brief encryption | Per-record AES-256-GCM before datastore writes | ACTIVE |
| Transport | HTTPS and TLS across browser, NoBS and required providers | ACTIVE |
| Password storage | bcrypt, cost factor 12, unique per-password salts | ACTIVE |
| Sessions | Opaque server-side sessions, not browser-readable JWT claims | ACTIVE |
| Session cookies | HttpOnly, Secure and SameSite protections | ACTIVE |
| Login protection | Rate limiting on repeated authentication attempts | ACTIVE |
| File archive | No persistent archive of original uploads | NONE |
| Analytics trackers | Advertising trackers, session recording, cross-site analytics | NONE |
| Error monitoring | Sentry, scrubbed of brief content and identity | ACTIVE |
| Security headers | HSTS, MIME-sniffing, framing, referrer and permissions controls | ACTIVE |
The services
involved are
named
NoBS uses specialized providers for specific operational jobs. We show the role of each provider instead of pretending the product runs in complete isolation.
AI
OpenAI
Brief processing and
relevant prior output.
SEARCH
Brave Search
Reference-discovery terms derived from a brief.
DATA
Upstash
Brief records (encrypted by NoBS) and operational account data.
HOST
Vercel
Application hosting
and compute.
EXPORT
ConvertAPI
Rendered output when PDF export is requested.
ERROR MONITORING
Sentry
Error reports, scrubbed.
No brief content.
SYSTEM EMAIL
Resend
Verification and account mail.
No brief content.
INFO EMAIL
Loops
News and notices.
No brief content.
PAY
Stripe
Payments and subscription data. No brief content.
Questions
deserve direct
answers
Read the standalone FAQ for plain-language answers about employees, uploads, encryption, deletion, payments and enterprise reviews.